
Statutory Foundations
Core Pillars of the Framework
A principle-based legal code transforming digital governance across Indian commerce.
Data Principal Centric
Citizens retain absolute ownership and control.
Purpose Limitation
Data collection restricted strictly to declared purposes.
Fiduciary Liability
Direct accountability for processor non-compliance.
Legal Taxonomy
The DPDP Legal Vocabulary
- Data Principal
- The individual whose personal data is processed.
- Data Processor
- Third parties processing data on the Fiduciary's behalf.
- Data Fiduciary
- The entity determining purpose and means of processing.
- Consent Manager
- Interoperable platform giving users unified consent access.
Enforcement Exposure
Statutory Penalties for Non-Compliance
₹250 Cr
Maximum financial penalty per breach instance
Applies to failure in adopting reasonable security safeguards under Section 8(5).
Section 6 Standards
Affirmative Consent Principles
Itemized Notice
Every purpose stated independently.
22 Languages
Notices in Schedule 8 tongues.
Unbundled
No pre-ticked acceptance boxes.
Easy Revocation
Withdrawal as easy as granting.
Section 9 Mandate
Safeguards for Children's Data
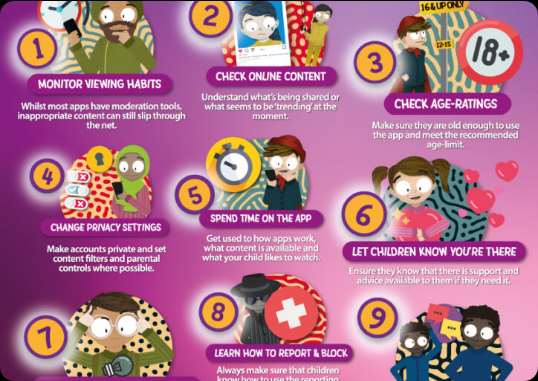
Verifiable Parental Consent
Mandatory verified consent before processing minor records.
Zero Behavioral Profiling
Absolute prohibition on tracking and behavioral ads for under-18s.
₹200 Crore Liability
Severe statutory fine structure for Section 9 non-compliance.
Sections 11–14
Enforceable Rights of Citizens
- Right to Access: Summary of personal data and processing activities.
- Right to Correction: Correction and updating of inaccurate data.
- Right to Erasure: Deletion when processing purpose is fulfilled.
- Right to Grievance: Accessible redressal before approaching DPBI.
- Right to Nominate: Transfer of rights upon death or incapacity.
Tiered Governance
Standard vs. Significant Fiduciary
Standard Data Fiduciary
- Clear notice and affirmative consent capture
- Reasonable data security safeguards
- Mandatory breach reporting to the DPBI
- Grievance redressal contact publication
Significant Fiduciary (SDF)
- Mandatory resident Data Protection Officer (DPO)
- Regular Data Protection Impact Assessments (DPIA)
- Periodic audits by independent data auditors
- Enhanced regulatory reporting obligations
Procurement & Technology
Tool Selection by Organization Scale
| Tier | Target Profile | Recommended Tools | Key Function |
|---|---|---|---|
| Small Entities | Clinics, schools, pathlabs, seed startups | CookieYes, Consently, Leegality | Plug-and-play consent notices & VPC forms |
| Mid-Market | Regional hospitals, scaling SaaS, retail | Redacto, IDfy Privy, Sprinto | Aadhaar redaction, vendor DPA, DSAR intake |
| Enterprise / SDF | Banks, telecoms, hospital chains | Securiti.ai, OneTrust, Privado | Continuous DSPM, code scanning, live RoPA |
Technical Safeguards
Engineering for Privacy Posture
Automatic Indian PII Redaction
Mask Aadhaar and PAN numbers in diagnostic reports.
Role-Based Access Controls
Strict least-privilege boundary across cloud databases.
72-Hour Breach Reporting
Mandatory timeline to report data incidents to the DPBI.
Execution Roadmap
Road to May 2027 Enforcement
Phase 01
Discovery
Data inventory and complete RoPA register.
Phase 02
Remediation
Notices, VPC workflows, and processor DPAs.
Phase 03
Tooling
DSAR automation and breach drill routines.
Phase 04
Enforcement
Full readiness for May 2027 statutory go-live.
Turn Privacy Into Trust
DPDP compliance is more than regulatory adherence—it is a competitive advantage in India's expanding digital economy.
Open for Discussion & Readiness Assessment